

Website and application security services: audits, hardening and malware clean-up
At AcmaSoft, we find and fix security weaknesses in websites, web applications and the servers behind them: code and configuration reviews against the OWASP Top 10, hardening, malware clean-up, firewalls, monitoring and secure update routines.
- Years of experience
- 17+
- Clients served
- 650+
- Projects delivered
- 2,000+
- Products shipped
- 300+
Most attacks use known, preventable weaknesses
Hacked websites rarely fall to sophisticated attacks. They fall to an outdated plugin, a form that accepts any file, an admin password reused elsewhere or a server nobody has patched. The same weaknesses appear again and again, which means they can be found and closed before someone uses them.
We review your application and its hosting the way an attacker would look at them, fix what we find in order of risk and set up routines that keep the site safe after we leave: updates, backups, monitoring and a short checklist for your team.
For a formal penetration test or a VAPT certificate required by a client or regulator, we work alongside a certified security firm of your choice and fix what it reports. Server care is covered under managed cloud, and testing before every release under QA and software testing.
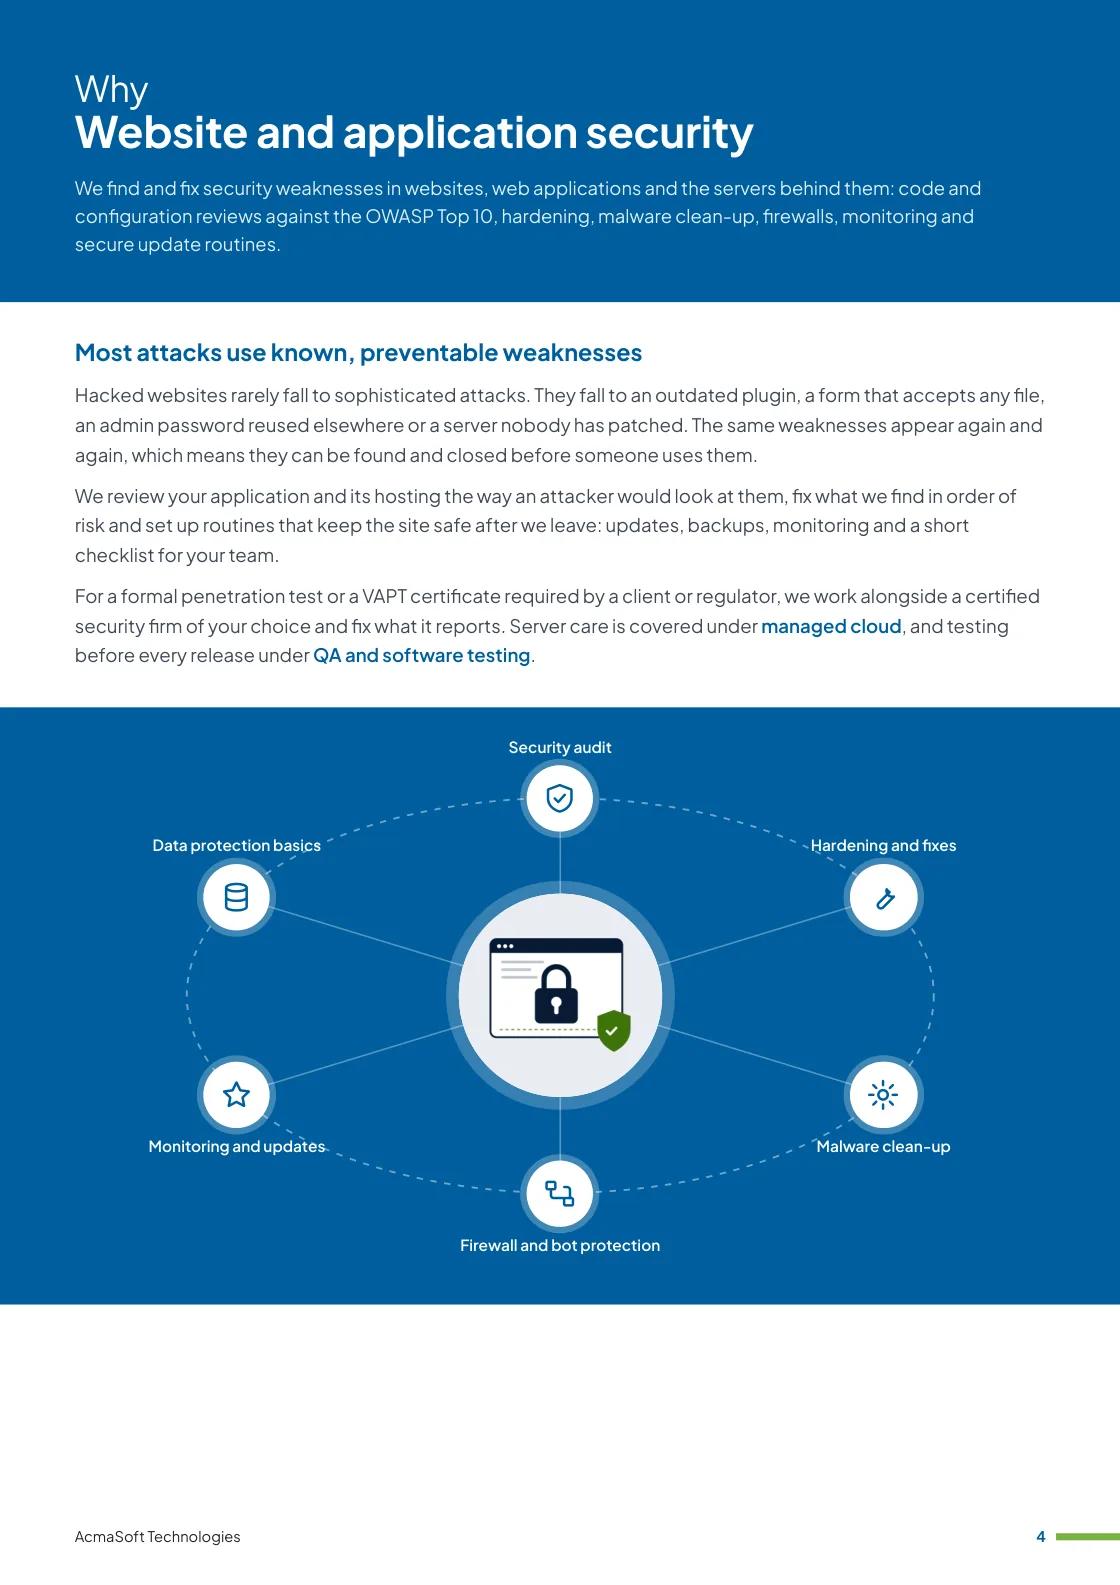
What you get with website and application security
- Security audit
- Hardening and fixes
- Malware clean-up
- Firewall and bot protection
- Monitoring and updates
- One named lead from first call to launch
- Support and improvements after launch
More in Software and app development
What our security service covers
Six areas that remove the common ways websites and applications are attacked.
-
Security audit
Know where you stand
A review of code, configuration, plugins, user accounts and hosting against the OWASP Top 10 and common CMS risks, with automated scans and manual checks.
Findings come with a risk rating and a clear fix.
-
Hardening and fixes
Closing the gaps
Secure headers, strict file permissions, safe upload handling, input validation, rate limits on logins and forms, and removal of unused code and accounts.
We fix issues in your code directly or work with your developers.
-
Malware clean-up
Recovering a hacked site
Removal of malware, backdoors and spam pages, restoration of clean files, blacklist removal requests and a review of how the attacker got in.
We close the entry point so the infection does not return.
-
Firewall and bot protection
Stopping attacks before they arrive
Web application firewall rules, Cloudflare setup, bot and spam protection on forms and rate limiting for logins and APIs.
Genuine visitors pass through without puzzles.
-
Monitoring and updates
Staying secure
File change monitoring, uptime and blacklist checks, scheduled updates for core, plugins and dependencies, and alerts when something looks wrong.
Monthly reports show what changed and what was blocked.
-
Data protection basics
Handling personal data carefully
Encryption in transit and at rest, least-privilege access, audit logs, data retention rules and cookie consent designed with GDPR and UK GDPR, CCPA and India’s Digital Personal Data Protection Act in mind.
We document the controls for your compliance records.
What to look for in a website security partner
Security work needs trust and clarity. Look for:
-
Fixes, not just reports
A team that can change the code and server settings, not only hand over a list of problems.
-
Honest scope
Clear about what an audit covers and when a certified penetration test is the right next step.
-
Ongoing care
Updates, backups and monitoring after the fix, so the same problem does not return.
Ways to work with us
Choose the model that fits your scope and budget for website and application security. Many clients start with one and move to another as the work grows.
-
Fixed price
A defined scope delivered for an agreed price and timeline, in milestones you approve.
- Best for
- Clear requirements, a fixed budget and a firm deadline.
- How it is priced
- One agreed price, paid in instalments tied to milestones.
-
Dedicated team
A team with a project lead that works only on your product, on the priorities you set.
- Best for
- Long-term products and roadmaps that change often.
- How it is priced
- A monthly fee per team member, based on role and seniority.
-
Time and material
You pay for the hours worked and can change the scope as you learn, in short iterations.
- Best for
- Requirements that are hard to fix up front, and ongoing improvements.
- How it is priced
- Hourly or daily rates by role, invoiced monthly against logged time.
Need DevOps engineers to join your own team instead?
Hire DevOps engineersWhat our clients say
More client reviews-
We rely on AcmaSoft's hosting services for our business-critical applications. The reliability of their servers and the uptime guarantee have exceeded our expectations.
Raj B Mumbai -
AcmaSoft's hosting solutions have grown with our business. The scalability of their services allows us to seamlessly expand without worrying about infrastructure constraints.
Isabella M London
Industries our software and app development team works in
Our software and app development team builds for businesses in these industries, and we adapt website and application security to each one's rules, systems and customers.


Technology we use
We choose the stack for your budget, goals and current systems. Each link explains how we work with that technology or product.
Not sure which technology fits your project? Ask one of our architects.
Talk to an architectWorking with international clients
Our team delivers remotely, so the questions that matter are when we can talk and how the work is run. Here are our office hours beside yours.
Our office hours Monday to Saturday, 9:30 am to 6:30 pm India time (IST)
Evening hours for North American clients, by arrangement: Monday to Friday, 6:30 pm to 9:30 pm India time
| Your region | Our hours in your time | Shared working hours |
|---|---|---|
| UKLondon | 4 am to 1 pm | 9 am to 1 pm |
| Central EuropeParis, Berlin | 5 am to 2 pm | 9 am to 2 pm |
| US EastNew York, Toronto | 11 pm to 8 am (next day) Evening hours to 11 am | 9 am to 11 am In our evening hours, by arrangement |
| US WestLos Angeles, Vancouver | 8 pm to 5 am (next day) Evening hours to 8 am | No overlap Early calls 7 am to 8 am, by arrangement |
| GulfDubai, Abu Dhabi | 8 am to 5 pm | 9 am to 5 pm |
| Singapore | 12 noon to 9 pm | 12 noon to 6 pm |
| Australia EastSydney, Melbourne | 3 pm to 12 midnight | 3 pm to 6 pm |
Our day ends before yours starts, so updates are waiting each morning and we agree call times with you.
Times follow daylight saving where your region uses it, against a working day of 9 am to 6 pm. Messages sent outside our hours are picked up when the team is back.
-
Remote delivery
Discovery, design, development and testing run remotely, with one named lead, a demo of working features at the end of each sprint and a staging site you can try.
-
How we stay in touch
Email, video calls and chat such as Slack, Microsoft Teams or WhatsApp, with the hours of overlap and meeting times agreed in the communication plan at the start.
-
Contracts and invoices
Proposals, contracts and invoices are in English and priced in US dollars, or in your own currency on request. A non-disclosure agreement can be signed before you share any details.
-
Privacy laws we design for
We design forms, consent and data handling with the law of your market in mind: GDPR and UK GDPR, CCPA and CPRA, PIPEDA, the UAE PDPL, the Australian Privacy Act, Singapore's PDPA and India's DPDP Act.
Questions about website and application security
Something else on your mind? Ask us directly and a specialist will reply.
Ask a questionIs a security audit the same as a penetration test?
No. Our audit reviews code, configuration and hosting against the OWASP Top 10 with scans and manual checks, and we fix what we find. A formal penetration test or VAPT certificate comes from a certified security firm; we can work with the firm you choose and fix its findings.
Our website has been hacked. What should we do first?
Change passwords for hosting, the CMS admin and email, keep a copy of the current files and database for investigation and contact us. We clean the site, find how the attacker got in and close that entry point.
Do you secure WordPress websites?
Yes. WordPress sites are a large part of our work: core and plugin updates, removal of unused plugins, file permissions, login protection, firewall rules and malware scanning.
Does this help with GDPR, UK GDPR or India's DPDP Act?
It helps with the technical side: encryption, access control, logging and data retention. Legal obligations such as notices and consent records should be reviewed with your legal adviser.
Can you check our app's APIs?
Yes. We review authentication, permission checks, input validation and rate limits on web and mobile APIs against the OWASP API Security Top 10.
Website and application security brochure
We find and fix security weaknesses in websites, web applications and the servers behind them: code and configuration reviews against the OWASP Top 10, hardening, malware clean-up, firewalls, monitoring and secure update routines.
Inside this brochure
- Most attacks use known, preventable weaknesses
- What our security service covers
- How a security project runs
- Technologies and solutions
- 2.8 MB
- 10 pages
- Services
You have downloaded from us before, so this one needs no form.
Get the brochure
Tell us who you are and the download starts straight away. We remember you on this device for 90 days, so you only fill this in once.
Your download has started.
If it does not start, download the brochure here. The links work for 15 minutes.
- Your reference
- Brochure
What you can do next
- Read it and share itShare the brochure with your team before you get in touch. It is free to read and share.
- Get a quote when you are readySix short questions on our request a quote page, and a reply within one business day.
Start your Website and application security project
Tell us what you are planning and a specialist will reply with next steps, a rough timeline and the questions we need answered.
- Emailsales@acmasoft.com
- Call+1 (707) 706 4092
- Prefer a call?
Thank you, your message is on its way.
It has reached our sales team, together with the page you sent it from.
- Your reference
- Budget
While we prepare your reply, here is the Website and application security brochure.
Download the brochure, Website and application security brochure, PDF, 2.8 MBWhat happens next
- A specialist gets in touchWithin one business day, by email or phone, with any questions about what you need.
- We talk it throughA short call about your goals, users, timeline and budget. We can sign an NDA first.
- You get a proposalScope, team, timeline and cost, with the engagement model that fits the work.